U.S. Data Privacy Laws 2026: What Businesses Need to Know Now
Anúncios
The landscape of data privacy in the United States is on the cusp of a monumental transformation. As of July 1, 2026, a comprehensive set of new U.S. data privacy laws will take full effect, impacting virtually every business operating within the nation. This isn’t merely an update; it’s a paradigm shift designed to grant consumers greater control over their personal information and hold businesses to higher standards of data stewardship. For enterprises of all sizes, from nascent startups to multinational corporations, understanding and preparing for these regulations is not just a legal obligation but a critical strategic imperative. Non-compliance could lead to significant financial penalties, reputational damage, and a loss of customer trust. This article serves as your definitive guide to navigating the complexities of the upcoming U.S. data privacy framework, outlining key provisions, practical steps for compliance, and the broader implications for the business world.
Anúncios
The Dawn of a New Era: Understanding the Core of U.S. Data Privacy Laws
For years, the United States has operated under a patchwork of sector-specific and state-level data privacy regulations, such as HIPAA for healthcare and the CCPA/CPRA in California. While these have laid important groundwork, the new federal legislation aims to create a more unified and robust framework, akin to Europe’s General Data Protection Regulation (GDPR) but tailored to the U.S. context. The primary goal is to empower individuals with more rights regarding their personal data and to impose clear responsibilities on organizations that collect, process, and store this information. This unified approach to U.S. data privacy is intended to simplify compliance for businesses operating across state lines, while simultaneously enhancing consumer protection nationwide.
Key Pillars of the New Legislation
While the final legislative text is extensive, several core principles underpin the new U.S. data privacy laws:
Anúncios
- Consumer Rights: Individuals will have expanded rights, including the right to access their data, correct inaccuracies, delete their data, and opt-out of the sale or sharing of their personal information for targeted advertising. These rights are fundamental to the new framework.
- Data Minimization: Businesses will be encouraged, and in many cases required, to collect only the personal data that is strictly necessary for the stated purpose. This moves away from the previous model of collecting as much data as possible.
- Purpose Limitation: Personal data collected for one purpose cannot be used for a significantly different, unrelated purpose without explicit consent or a clear legal basis.
- Data Security: Organizations will be mandated to implement reasonable security measures to protect personal data from unauthorized access, disclosure, alteration, and destruction. The definition of ‘reasonable’ will likely evolve with technological advancements.
- Transparency and Accountability: Businesses must be transparent about their data collection and processing practices, often through clear and accessible privacy policies. They will also be held accountable for demonstrating compliance.
- Consent Requirements: The new laws will likely strengthen consent requirements, particularly for sensitive personal data or certain types of data processing. Implied consent may no longer suffice in many scenarios.
These pillars collectively form the bedrock of the enhanced U.S. data privacy landscape. Businesses must move beyond a reactive compliance mindset to a proactive, privacy-by-design approach.
Who is Affected? Scope and Applicability of the New U.S. Data Privacy Laws
One of the most critical aspects for businesses to understand is whether these new U.S. data privacy laws apply to them. The legislation is designed to have broad applicability, ensuring comprehensive protection for U.S. residents. Generally, if your business collects, processes, stores, or sells the personal data of U.S. consumers, you are likely subject to these regulations. This includes:
- Businesses Operating in the U.S.: Any entity physically located or primarily operating within the United States that handles personal data.
- Businesses Targeting U.S. Consumers: Even if your business is based internationally, if you actively market to, collect data from, or offer services to residents of the U.S., you will likely fall under the purview of these laws.
- Data Processors and Controllers: The laws typically differentiate between ‘data controllers’ (those who determine the purposes and means of processing personal data) and ‘data processors’ (those who process personal data on behalf of a controller). Both roles carry significant responsibilities, though the specifics may differ.
- Size Thresholds: While some state laws (like CCPA) have revenue or data volume thresholds, the new federal legislation aims for broader coverage. It’s anticipated that only very small businesses with minimal data processing activities might be exempt, but this will depend on the final legislative details. It’s safer to assume applicability than to assume exemption when it comes to U.S. data privacy.
It is imperative for every business to conduct an internal assessment to determine the extent of their obligations under these new U.S. data privacy laws. This assessment should involve legal counsel specializing in data privacy to ensure accurate interpretation and application.
Preparing for Compliance: A Strategic Roadmap for Businesses
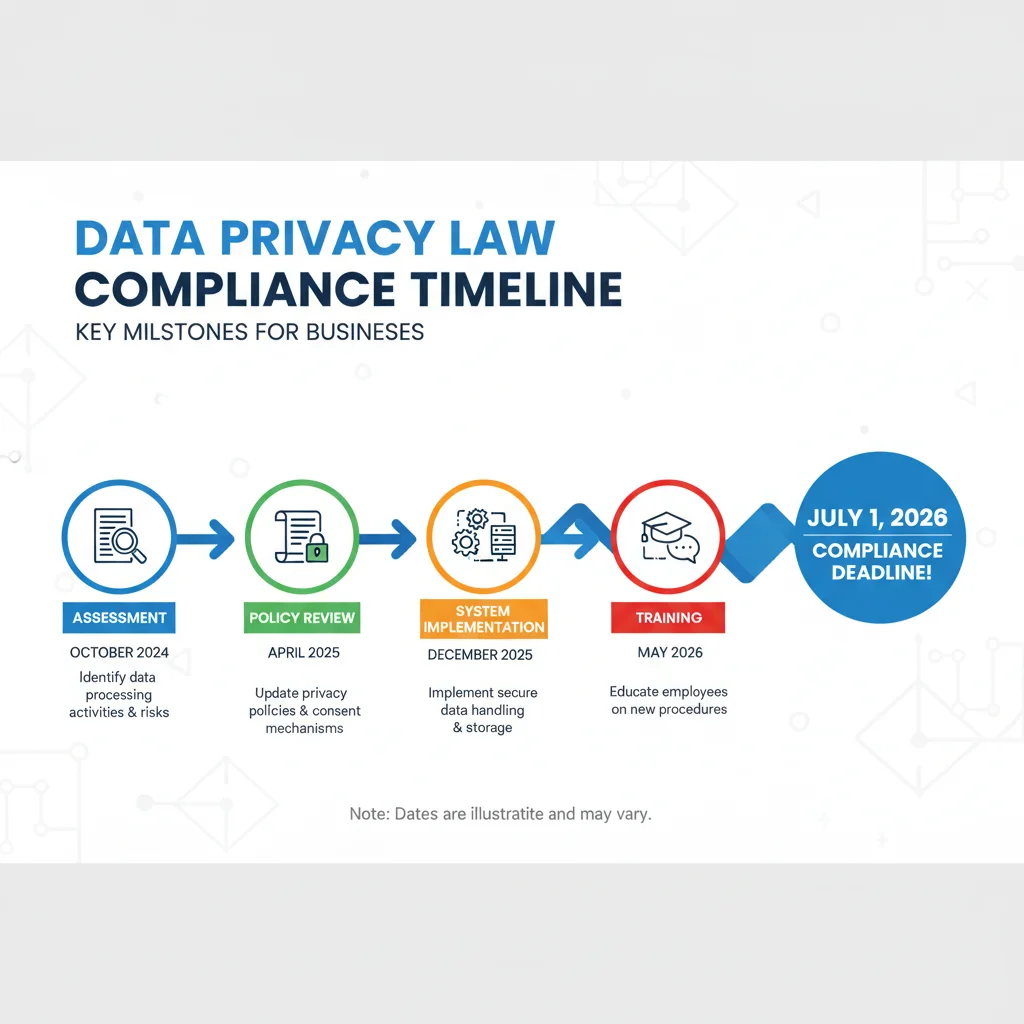
With the July 1, 2026 deadline approaching, businesses have a critical window to prepare. Compliance with the new U.S. data privacy laws is not a one-time project but an ongoing commitment. Here’s a strategic roadmap to guide your preparation:
1. Data Inventory and Mapping
The first step is to understand what data you have. Conduct a thorough data inventory to identify all personal data collected, where it is stored, how it is used, who has access to it, and how long it is retained. This data mapping exercise is foundational for any privacy compliance program. Without knowing what data you possess, you cannot adequately protect it or respond to consumer requests.
2. Review and Update Privacy Policies
Your current privacy policy will almost certainly need significant revisions. It must clearly and concisely explain your data practices in accordance with the new U.S. data privacy requirements. This includes detailing consumer rights, how to exercise them, types of data collected, purposes of collection, third-party sharing, and data retention periods. Ensure it is easily accessible on your website and other relevant platforms.
3. Implement Mechanisms for Consumer Rights
Develop robust processes and systems to handle consumer requests regarding their data. This includes:
- Access Requests: How will you provide individuals with copies of their data?
- Correction Requests: How will you update inaccurate personal information?
- Deletion Requests: How will you securely and completely erase personal data when requested, while adhering to any legal retention obligations?
- Opt-Out Mechanisms: Implement clear and easy-to-use methods for consumers to opt-out of data sales, sharing for targeted advertising, or specific data processing activities. This might involve a dedicated web form, a privacy dashboard, or clear links on your website.
4. Enhance Data Security Measures
Review and bolster your existing cybersecurity infrastructure. The new U.S. data privacy laws will likely require ‘reasonable’ security measures, which implies a continuous assessment of risks and implementation of appropriate safeguards. This may include:
- Encryption for data at rest and in transit.
- Access controls and multi-factor authentication.
- Regular security audits and penetration testing.
- Incident response plans for data breaches.
- Employee training on data security best practices.
5. Update Vendor and Third-Party Contracts
If you share personal data with third-party vendors, service providers, or partners, their compliance is also your responsibility. Review all existing contracts to ensure they include robust data protection clauses that align with the new U.S. data privacy laws. This includes provisions for data processing agreements, security obligations, audit rights, and breach notification requirements. Future contracts must incorporate these elements from the outset.
6. Conduct Data Protection Impact Assessments (DPIAs)
For new projects or technologies that involve high-risk processing of personal data, conducting a Data Protection Impact Assessment (DPIA) will likely become a requirement. A DPIA helps identify and mitigate privacy risks before they materialize, demonstrating a proactive approach to U.S. data privacy compliance.
7. Employee Training and Awareness
Your employees are your first line of defense. Implement comprehensive training programs to educate all staff members who handle personal data about the new U.S. data privacy laws, their roles and responsibilities, and best practices for data handling and security. Regular refreshers are crucial to maintain awareness.
8. Appoint a Privacy Officer or Designate a Responsible Party
Consider appointing a Data Protection Officer (DPO) or designating an individual or team responsible for overseeing your organization’s privacy program. This central point of contact will be crucial for managing compliance efforts, responding to regulatory inquiries, and handling consumer requests.
The Impact on Business Operations and Innovation
The new U.S. data privacy laws will undoubtedly have far-reaching implications beyond just legal compliance. They will influence business operations, marketing strategies, product development, and customer relations.
Marketing and Advertising
Targeted advertising, a cornerstone of digital marketing, will face significant changes. The ability for consumers to opt-out of data sharing for this purpose means businesses will need to rethink their acquisition and retention strategies. Contextual advertising, first-party data strategies, and building direct relationships with customers will become even more valuable.
Product Development
The principle of ‘privacy by design’ will become paramount. This means integrating privacy considerations into the very earliest stages of product and service development, rather than as an afterthought. Products and services that inherently protect user privacy will gain a competitive advantage.
Customer Trust and Brand Reputation
In an increasingly privacy-aware world, demonstrating a strong commitment to protecting customer data can be a significant differentiator. Businesses that are transparent, proactive, and respectful of user privacy will build greater trust and enhance their brand reputation, fostering stronger customer loyalty. Conversely, privacy breaches or non-compliance can severely damage a brand.
Data Analytics and AI
The new regulations will also impact how businesses leverage data for analytics and artificial intelligence. While data-driven insights remain crucial, organizations will need to ensure that their data collection and processing for AI models comply with consent requirements, data minimization principles, and transparency obligations. Anonymization and pseudonymization techniques will become more important for ethical and legal data use.
Common Pitfalls to Avoid in U.S. Data Privacy Compliance
As businesses embark on their compliance journey for the new U.S. data privacy laws, several common mistakes can undermine their efforts. Being aware of these pitfalls can help organizations navigate the transition more smoothly:
- Underestimating the Scope: Many businesses incorrectly assume the laws won’t apply to them or that their existing state-level compliance is sufficient. The federal nature of these new laws means a broader reach.
- Delaying Action: Privacy compliance is complex and time-consuming. Waiting until the last minute will lead to rushed, inadequate implementations and increased risk of non-compliance.
- Treating it as a Purely IT or Legal Problem: While IT and legal departments are crucial, data privacy is a cross-functional issue that requires involvement from marketing, sales, HR, product development, and senior leadership.
- Focusing Only on Documentation: While updated policies and procedures are essential, true compliance requires operationalizing these documents through systems, processes, and employee behavior.
- Ignoring Third-Party Risk: A significant portion of data breaches and compliance failures originate from third-party vendors. Neglecting to vet and contractually bind third parties to privacy standards is a major oversight.
- Lack of Ongoing Monitoring: Compliance is not a one-time project. The regulatory landscape evolves, as do business practices and technologies. Continuous monitoring, auditing, and adaptation are necessary.
- Inadequate Employee Training: Even the most robust policies are ineffective if employees are not properly trained and aware of their responsibilities regarding personal data. Human error remains a leading cause of data incidents.
Avoiding these pitfalls requires a holistic, integrated, and continuous approach to U.S. data privacy management.
The Future of Data Privacy in the U.S.
The introduction of these new U.S. data privacy laws marks a significant milestone in the ongoing global conversation about data rights and corporate responsibility. While the immediate focus is on compliance by July 1, 2026, it’s important to view this as part of a larger, evolving trend. We can expect:
- Increased Enforcement: With a unified federal framework, enforcement actions are likely to become more frequent and impactful.
- Technological Advancements: The demand for privacy-enhancing technologies (PETs) will grow, offering new solutions for anonymization, secure data sharing, and consent management.
- Greater Consumer Awareness: As these laws empower individuals, consumers will become more aware of their rights and more likely to exercise them, putting pressure on businesses to be transparent and compliant.
- Global Harmonization (Potential): While distinct, the new U.S. laws may also contribute to a gradual harmonization of global data privacy standards, simplifying compliance for multinational corporations in the long run.
Businesses that embrace these changes not just as a burden, but as an opportunity to build trust and innovate responsibly, will be well-positioned for success in the evolving digital economy. Proactive engagement with U.S. data privacy is no longer optional; it’s fundamental to sustainable business growth.
Conclusion: Your Call to Action for U.S. Data Privacy Compliance
The July 1, 2026 deadline for the new U.S. data privacy laws is rapidly approaching. This comprehensive legislation represents a profound shift in how personal data is handled across the nation, demanding immediate and sustained attention from all businesses. From understanding the core consumer rights to implementing robust data security measures and updating third-party contracts, the path to compliance is multifaceted and requires strategic planning, cross-departmental collaboration, and continuous effort.
Ignoring these impending changes is not an option. The potential for significant financial penalties, irreparable damage to brand reputation, and erosion of customer trust far outweighs the investment required for compliance. Instead, view this as an opportunity to strengthen your data governance practices, build deeper trust with your customers, and position your organization as a leader in responsible data stewardship.
Start your compliance journey today. Conduct thorough assessments, engage legal and technical experts, educate your workforce, and integrate privacy by design into every aspect of your operations. By taking proactive steps now, your business can not only meet the requirements of the new U.S. data privacy laws but also thrive in an increasingly privacy-conscious world.